AI Agents Without Guardrails Are a Liability
We harden your AI agents for production — permission scoping, memory isolation, audit trails, and monitoring that keep your agents operating within defined boundaries.


Most AI Agents Are One Prompt Away From a Security Incident
Teams deploy agents with full API access, no permission scoping, and prompts that can be jailbroken with a single crafted message. The agent can send emails, modify databases, and call external services — all without any boundary on what it is allowed to do.
Security is not a feature you add after launch. It is the architecture that separates a production system from a prototype. We harden agents before they touch production data — because once an unguarded agent acts, the damage is already done.
Six Security Layers for AI Agents
Each layer closes a distinct attack surface. Skip one, and the agent is exposed.
Autonomy Boundaries
Every agent ships with explicitly defined permission scopes. What it can do, what requires human approval, and what is completely off-limits. Zero ambiguity.
Credential & Secret Management
API keys, tokens, and credentials are never hardcoded. Encrypted at rest, rotated automatically, and scoped to minimum required permissions per agent function.
Audit Trails
Every action an agent takes is logged with timestamp, context, and outcome. Full forensic trail for compliance, debugging, and internal reviews.
Memory Isolation
Agent memory is namespaced per user, per session, per function. No cross-contamination. No data leakage between contexts.
RAG Security
Retrieval-augmented generation with access-controlled knowledge bases. Agents only see what they are explicitly authorized to retrieve.
Self-Hosted Boundaries
Everything runs on your infrastructure. No data leaves your VPC. Network-level isolation for agents handling sensitive operations.
Memory Hardening Process
Five steps from vulnerable to production-hardened.
Risk Assessment
Map your agent's operational surface: what data it touches, what systems it calls, what actions it can take. Identify every trust boundary.
Permission Scoping
Define least-privilege permissions per agent function. Scope API keys, database access, and tool permissions to exactly what each agent needs.
Prompt Hardening
Harden system prompts against injection, jailbreaking, and prompt leakage. Guardrail prompts that enforce the agent's operational boundaries.
Memory Architecture
Design memory isolation: per-user, per-session namespaces. Separate short-term context from long-term knowledge bases. Encrypted at rest.
Monitoring & Alerting
Deploy monitoring on every agent action. Anomaly detection on out-of-scope behavior. Real-time alerts when an agent approaches or crosses a boundary.
AI Automation Success Stories
Explore how we've architected custom AI automations and Agentic systems that deliver immediate ROI and scalable growth for our clients.
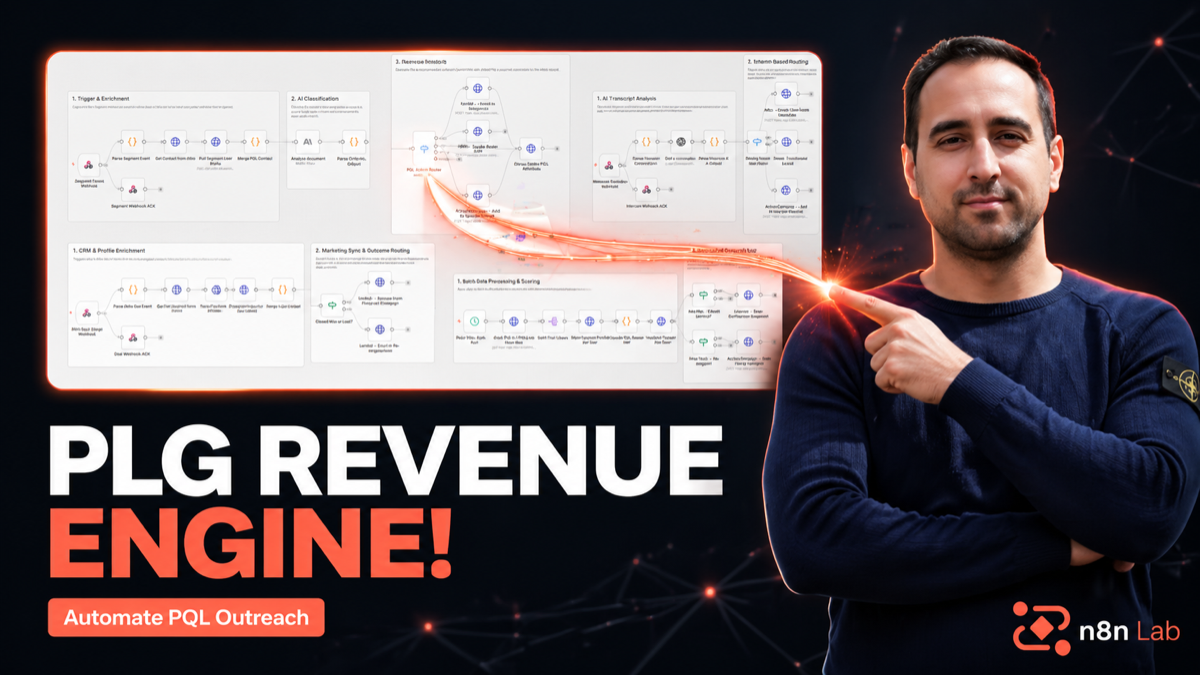
PLG Revenue Engine
Connecting Product Data to Revenue With AI Automation
Focus Physiotherapy
OpenClaw turned intake friction into a guided booking flow
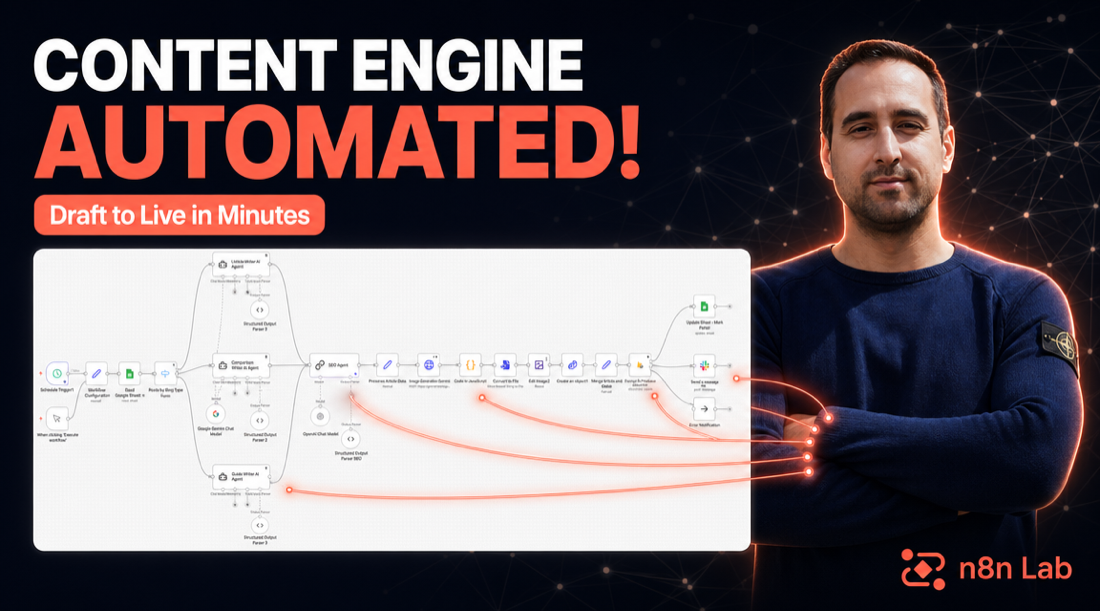
n8n Blog Production
Five-agent content engine for automated blog publishing
AI Voice Agents for B2B SaaS
Scaling Outbound Sales Process powered by n8n, Twilio, and Vapi
CRM Agent for Digital Agency
Discover How n8n Workflows Empower BDRs to Focus Just on Closing Deals
The Collecting Group
AI Voice Agent & Automation Strategy
How We Work
From audit to ongoing surveillance. Four phases to hardened agents.
Security Audit
We audit your agent architecture across all six security layers, identify vulnerabilities, and prioritize hardening actions by risk level.
Architecture Design
We design the hardened architecture: permission scoping, credential management, memory isolation, audit trails, and monitoring.
Implementation
We implement the hardening — prompt engineering, infrastructure configuration, monitoring deployment. Your agents ship production-ready.
Ongoing Monitoring
Continuous surveillance of agent behavior. Regular security reviews. Anomaly detection and automated alerting when boundaries are tested.
Why n8n Lab for Agent Security
Security Is Architecture, Not an Afterthought
We design agent security from the first architecture diagram. Permission scoping, credential management, and audit trails are built into the system, not retrofitted after a breach.
Self-Hosted Means You Control the Perimeter
Your agents, your servers, your network. No third-party cloud touching your data. Network-level isolation, VPC boundaries, and firewall rules you define and control.
Guardrails That Actually Work
Prompt hardening against injection and jailbreaking. Explicit permission scopes per agent function. Escalation paths when an agent approaches a boundary. Monitoring that catches anomalies before they become incidents.
Memory Isolation by Design
Per-user, per-session, per-function memory namespacing. No cross-contamination. Encrypted at rest. Knowledge bases with access controls that agents cannot bypass.
FAQ
Why do AI agents need security hardening specifically?▾
What is memory isolation and why does it matter?▾
How do you prevent prompt injection and jailbreaking?▾
Can our compliance requirements (SOC 2, HIPAA, GDPR) be met?▾
How do you monitor agents for security incidents after deployment?▾
Harden Your Agents Before They Touch Production
Start with a security audit. We will assess your agent architecture, identify vulnerabilities, and give you a hardening roadmap — same call, no commitment.